Could your business handle a cyberattack without losing important data or disrupting daily operations? Are your current security controls strong enough to protect your employees, systems and customer information?
Cybersecurity readiness means having the right security controls, trained employees and response plans to identify, prevent and recover from cyber threats. A practical cybersecurity readiness checklist helps businesses identify security gaps and improve their overall protection.
In this guide, we explore essential cybersecurity checks, common business security weaknesses and practical steps to improve cyber readiness. You will also learn how to assess your organisation’s security posture and prepare for potential cyber incidents.
What Is Cybersecurity Readiness?
Cybersecurity readiness is an organisation’s capacity to secure, detect, answer to and recover from cyber threats.
It involves more than installing antivirus software or setting strong passwords. Businesses need a complete approach that covers technology, people, processes and risk management.
A strong business cybersecurity strategy helps organisations:
- Protect sensitive business and customer data.
- Identify security weaknesses before attackers exploit them.
- Reduce operational disruption.
- Improve employee security awareness.
- Respond effectively to cyber incidents.
- Maintain business continuity.
Why Is Cybersecurity Readiness Important for Businesses?
Cyber threats can affect businesses of every size. Weak passwords, outdated software, poor access controls and untrained employees can create opportunities for attackers.
Without proper preparation, a security incident may result in:
- Financial losses and unexpected recovery costs.
- Unauthorised access to business systems.
- Customer data exposure.
- Operational downtime.
- Reputational damage.
- Compliance and reporting challenges.
A regular cybersecurity readiness assessment helps businesses understand their current security position and prioritise improvements.
Practical Cybersecurity Readiness Checklist for Businesses
Use the following IT security checklist to review important areas of your organisation’s security.
| Security Area | Readiness Check |
| Password Security | Are strong and unique passwords enforced? |
| Multi-Factor Authentication | Is MFA enabled on important accounts? |
| Data Protection | Is sensitive business data encrypted? |
| Software Updates | Are systems regularly patched? |
| Email Security | Are suspicious emails and attachments monitored? |
| Endpoint Security | Are business devices protected? |
| Network Security | Are firewalls and network controls configured? |
| Data Backups | Are backups maintained and tested? |
| Employee Training | Do employees receive cybersecurity awareness training? |
| Incident Response | Is there a documented incident response plan? |
| Access Management | Are user permissions reviewed regularly? |
| Third-Party Security | Are supplier and service provider risks assessed? |
This checklist provides a starting point. Each organisation should adapt it according to its business operations, technology and risk exposure.
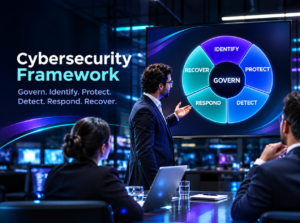
7 Key Areas Every Business Should Review
A checklist is useful, but businesses also need to understand what each security area involves.
1. Identity and Access Management
Review who can access your business systems, applications and sensitive information.
Use Multi-Factor Authentication (MFA), strong passwords and role-based access controls. Deactivate inactive accounts and review management permissions regularly.
2. Network and Infrastructure Security
Secure your business network against unauthorised entry and doubtful activity.
Review firewall configurations, secure remote access, network segmentation and connected devices. Regular network security assessments can help identify weaknesses.
3. Data Protection and Backup
Identify your critical business information and protect it from loss, theft or unauthorised access.
Use encryption, secure storage and regular backups. Test backup restoration to confirm that important information can be recovered when needed.
4. Application and Endpoint Security
Business applications, laptops, servers and mobile devices can become entry points for cyber threats.
Keep software updated, remove unnecessary applications and use endpoint protection to detect suspicious activities.
5. Employee Cybersecurity Awareness
Employees play an important role in business security.
Provide regular training on phishing emails, suspicious links, password protection, social engineering and safe data handling.
6. Third-Party and Cloud Security
External vendors and cloud platforms may have access to important business systems.
Review supplier security practices, access permissions, data handling procedures and contractual security responsibilities.
7. Incident Response and Business Continuity
Prepare a documented cyber incident response plan that explains what employees and security teams should do during an attack.
Define responsibilities, reporting procedures, communication channels and recovery steps. Test the plan through regular exercises.
How to Conduct a Cybersecurity Readiness Assessment
A cybersecurity readiness assessment helps organisations understand whether their existing security controls are effective.
Follow these practical steps:
- Identify Critical Assets: List important systems, applications, networks and business data.
- Assess Security Risks: Identify potential threats, vulnerabilities and their business impact.
- Review Existing Controls: Evaluate access management, endpoint protection, network security and data protection.
- Check Employee Awareness: Review training programmes and security reporting procedures.
- Evaluate Incident Response: Check whether your business can detect, contain and recover from an incident.
- Prioritise Improvements: Address high-risk security gaps first.
- Monitor Progress: Review security performance and repeat assessments regularly.
How Often Should Businesses Review Their Cybersecurity Readiness?
Cybersecurity readiness is an ongoing process, not a one-time activity.
| Review Activity | Suggested Frequency |
| Security Monitoring | Continuous |
| Software and Security Updates | Regularly as updates are released |
| User Access Review | Quarterly or after role changes |
| Employee Awareness Training | Regularly |
| Vulnerability Assessment | Periodically and after major changes |
| Backup Recovery Testing | Regularly |
| Incident Response Exercises | At least annually and when significant changes occur |
| Overall Security Assessment | Annually or following major business changes |
The exact schedule should reflect your organisation’s risk level, operational needs and applicable security requirements.
Common Signs Your Business Is Not Cyber Ready
Your organisation may need to improve its security posture if:
- Employees share passwords or use weak credentials.
- Important systems run outdated software.
- Backups are not tested regularly.
- No documented incident response plan exists.
- Security alerts are not investigated.
- Former employees still have active accounts.
- Third-party security risks are not reviewed.
- Employees cannot recognise common phishing attempts.
Identifying these weaknesses early allows businesses to take corrective action before they become larger security problems.
How CyberWaze Global Helps Improve Business Cyber Readiness
Building cyber resilience requires the right combination of security strategy, technical protection and ongoing risk management.
CyberWaze Global supports organisations through cybersecurity consulting and managed security capabilities designed to strengthen their security posture.
Its service areas include:
- Strategy Risk & Compliance: Identify risks and strengthen security governance.
- Cyber Defense: Improve threat observation and security functioning.
- Infrastructure & OT/IoT Security: Protect business infrastructure and connected environments.
- Digital Identity: Strengthen identity and access management.
- Application & Data Security: Protect applications and sensitive information.
- Managed Security: Support ongoing security management and monitoring.
Businesses can use professional cybersecurity support to identify weaknesses, improve security controls and develop a more structured approach to cyber risk.
Cyber Awareness: Build a Security-Ready Workforce
Cyber awareness helps employees recognise emerging threats, phishing attempts and digital risks.
Watch Our Latest CyberStudio Podcast
Discover insights on AI and women’s growing role in cybersecurity.
Latest Cybersecurity Updates from CyberWaze Global
Follow CyberWaze Global for cybersecurity insights, awareness updates and practical recommendations to help businesses stay informed about emerging threats.
Explore our latest social media updates
Conclusion
Cybersecurity readiness is essential for protecting business operations, sensitive information and digital infrastructure. Regular security assessments, employee training, strong access controls and tested incident response plans help organisations prepare for evolving cyber threats. CyberWaze Global helps businesses strengthen their cybersecurity capabilities through professional security consulting and managed security solutions.
Frequently Asked Questions
Q1. What is a cybersecurity readiness checklist?
A cybersecurity readiness checklist is a set of security checks used to evaluate an organisation’s protection, identify weaknesses and improve preparedness against cyber threats.
Q2. How can I check if my business is cyber ready?
Review your passwords, access controls, network security, data backups, employee awareness, vulnerability management and incident response procedures.
Q3. What are the most important cybersecurity controls for businesses?
Important controls include MFA, endpoint protection, firewalls, secure backups, email security, access management and continuous security monitoring.
Q4. What is the difference between cybersecurity readiness and cyber resilience?
Cybersecurity readiness focuses on preparing an organisation to handle threats. Cyber resilience focuses on maintaining essential operations and recovering when security incidents occur.
Q5. Why should businesses conduct regular cybersecurity assessments?
Regular assessments help identify new vulnerabilities, evaluate security controls, prioritise risks and maintain effective protection as business technology changes.